Showing posts with label types. Show all posts
Showing posts with label types. Show all posts
Wednesday, March 11, 2015
Upload all file types to any Google Account
Over the next few days we will be rolling out an expansion to the feature set of the Google Documents List API. Third-party applications may now upload files of any type to any Google Account. Previously, this was only possible for Google Apps for Business users.
This feature allows developers to roll out their solutions to all Google Docs users. For instance, it’s now possible for developers to build applications that allow all users to back up files from their local hard drive to the cloud. There are a variety of other possible uses for this feature, and some examples include revision control and file distribution. Third-party applications (such as those on the Google Apps Marketplace) can also now use Google Docs as the primary place to store their data without the hassle of creating different solutions for customers of Google Apps for Business versus the free edition of Google Apps.
After they are uploaded, files are available in the Google Docs interface:

To enable uploads for all file types, developers must use the resumable upload feature of the API, and also pass in the
We have also added checksums to all files that are not converted to a native Google Docs format. This means that if you upload a file type we cant convert, or if you choose not to convert a file to a native format, a checksum is now available to help guarantee the integrity of the file between storage and retrieval.
We are also in the process of adding checksums to all previously uploaded unconverted files. Due to the popularity of uploading unconverted files, processing this backlog will take some time to complete.
We’ve recently made a lot of improvements to the documentation that should make implementing all of this easier. For further help, please have a look in the forum.
Read more »
This feature allows developers to roll out their solutions to all Google Docs users. For instance, it’s now possible for developers to build applications that allow all users to back up files from their local hard drive to the cloud. There are a variety of other possible uses for this feature, and some examples include revision control and file distribution. Third-party applications (such as those on the Google Apps Marketplace) can also now use Google Docs as the primary place to store their data without the hassle of creating different solutions for customers of Google Apps for Business versus the free edition of Google Apps.
After they are uploaded, files are available in the Google Docs interface:
To enable uploads for all file types, developers must use the resumable upload feature of the API, and also pass in the
?convert=false URL parameter.We have also added checksums to all files that are not converted to a native Google Docs format. This means that if you upload a file type we cant convert, or if you choose not to convert a file to a native format, a checksum is now available to help guarantee the integrity of the file between storage and retrieval.
We are also in the process of adding checksums to all previously uploaded unconverted files. Due to the popularity of uploading unconverted files, processing this backlog will take some time to complete.
We’ve recently made a lot of improvements to the documentation that should make implementing all of this easier. For further help, please have a look in the forum.
Want to weigh in on this topic? Discuss on Buzz

Monday, March 9, 2015
Documents List API now supports more file types
We are happy to announce that we have recently launched support for creating and managing revisions for arbitrary file types in the Documents List API. Prior to this, the Documents List API only allowed developers to create and query revisions of Google Docs files.
This opens up the API for a number of exciting use cases. For example, a developer could use Google Docs as the cloud-based back-end for a content-management system with versioning. Another possibility would be for developers to provide file history or file playback in their sync clients.
Please note, however, that while all users can use the API to query and manage revisions, currently only Google Apps Premier users can upload arbitrary file types via the API. All users are still able to upload arbitrary files types via the Google Docs web interface.
For more information on how to use this new feature, please see the updated release notes and updated documentation.
Read more »
This opens up the API for a number of exciting use cases. For example, a developer could use Google Docs as the cloud-based back-end for a content-management system with versioning. Another possibility would be for developers to provide file history or file playback in their sync clients.
Please note, however, that while all users can use the API to query and manage revisions, currently only Google Apps Premier users can upload arbitrary file types via the API. All users are still able to upload arbitrary files types via the Google Docs web interface.
For more information on how to use this new feature, please see the updated release notes and updated documentation.
Want to weigh in on this topic? Discuss on Buzz
Tuesday, February 17, 2015
Types Of Hackers
 |
| Types Of Hackers |
Script Kiddies, in a word are noobs. They are the people who use tools, scripts, methods and programs created by real hackers. They are the ones who dont know how a system works but are still able to exploit it with previously available tools, not by walking in the footsteps of actual Hackers but simply copying what they did and using it for malicious purposes. A script kiddie is that one annoying kid in class, who pisses off everyone else. Dont be that guy.
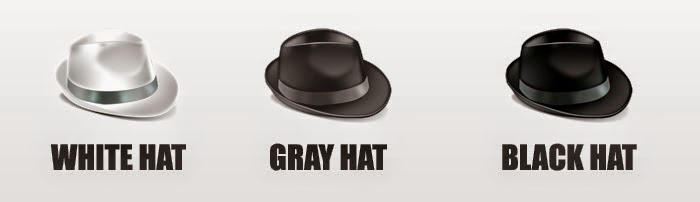
White Hat Hacker:
White Hat hackers or Penetration testers are the good guys who hack for security purposes. Although what they do is pretty much the same as bad guys, but a world of difference arises when it comes to ethics. The main aim of a Whitehat hacker is to improve the security of a system by finding security flaws and fixing it before the bad guys find and exploit it. They are usually officially employed by organizations and companies to protect their virtual assets from coming to harm. The may work also individually to make the cyber space more secure, kind of a voluntary worldwide community service. An example of this is the team behind the (in)famous Hacking Tool known as Metastasis who work tirelessly reporting new security flaws and their fixes in various software.
This website only concentrates on white-hat hacking and helps you to learn how to Hack for the welfare of everyone.
Black Hat Hacker:
BlackHat hackers are our enemies. They are the bad guys, cyber criminals who have malicious intents. These are the hackers who steal money or valuable data, infect systems with viruses, Trojans and malware etc. These are the ones who gave the world of Hacking a bad reputation and it is up to us, the whitehats to bring them down. They use their hacking skills for illegal purposes with unethical goals and sometimes just to watch the world burn. If ever you are attracted to the Dark Side of Hacking, ask yourself this : "Is a night of glory really worth a lifetime behind bars? ". If a person can get over half a dozen years sentence for copying images (fact), skys the limit when it comes to convicting cyber criminals.
GreyHat hackers:
These are the hackers who may work offensively or defensively, depending on the situation. They belong to the neutral zone. Hackers who dont have malicious intentions but still like to break into third-party system just for the thrill and fun or maybe just to announce a new owned vulnerability in a wild and supposedly heroic way. Nobody like a Show Off and the GreyHats do just that. Breaking into vital databases, say for example one containing Credit Card information is just as illegal as actually stealing them. So, even fooling around like this can land you in jail.
Hacktivists:
These are the hackers who use their hacking skills for protesting against injustice and attack a target system or websites to popularize a notion or gather attention to a specific case for rectification. They are vigilantes, The dark knights of the Hacking universe. This is where good intentions collide with the law, for Hacktivists may or may not carry out illegal activities to get their point across to the world. They include outlaws who deliver their own brand of rough justice, they are usually experts confident in their stealth skills so as not to get caught.
Subscribe to:
Posts (Atom)